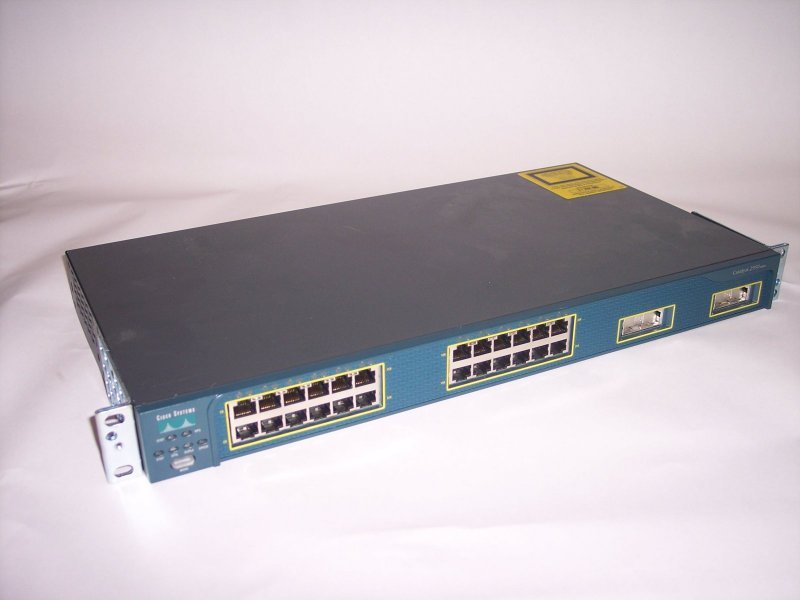
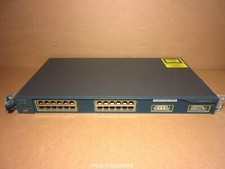
CISCO WS-C2950G-24-EI 24x 10/100 ports 2x 1000BASE-X ports
Dear customer,
When there might be a difference between the automatic generated specifications by the system, and the hand written/typed description, then please be aware that the only correct description is what's written by our selves here in the description.
Specifications above might be slightly different.
Thanks for your understanding.
CISCO WS-C2950G-24-EI 24x 10/100 ports 2x 1000BASE-X ports 10/100Mbps + 1000Mbps
P/N: WS-C2950G-24-EI
ModelBrand CISCOModel WS-C2950G-24-EI SpecStandards IEEE 802.1x support
IEEE 802.1w
IEEE 802.1s
IEEE 802.3x full duplex on 10BASE-T, 100BASE-TX, and 1000BASE-T ports
IEEE 802.1D Spanning-Tree Protocol
IEEE 802.1p class-of-service (CoS) prioritization
IEEE 802.1Q VLAN
IEEE 802.3 10BASE-T specification
IEEE 802.3u 100BASE-TX specification
IEEE 802.3ab 1000BASE-T specification
IEEE 802.3ad
IEEE 802.3z 1000BASE-X specification
RMON I and II standards
SNMPv1, SNMPv2c, SNMPv3 (planned future support for v3)Ports 24 x 10/100 ports
2 x 1000BASE-X portsSpeed 10/100Mbps + 1000MbpsMAC Address Table Up to 8000Buffer Memory 8 MB memory architecture shared by all ports
Up to 16 MB SDRAM and 8 MB Flash memorySecurity Filtering of incoming traffic flows based on Layer 2, Layer 3 or Layer 4 access control parameters (ACPs) prevents unauthorized data flows.
The following Layer 2 ACPs or a combination can be used for security classification of incoming packets: source Media Access Control (MAC) address, destination MAC address, and 16-bit Ethertype.
The following Layer 3 and Layer 4 fields or a combination can be used for security classification of incoming packets: source/destination IP address, TCP source/destination port number, User Datagram Protocol (UDP) source, or destination port number. ACLs can also be applied to filter based on DSCP values.
Time-based ACLs allow configuration of differentiated services based on time-periods.
Private VLAN edge provides security and isolation between ports on a switch, ensuring that voice traffic travels directly from its entry point to the aggregation device through a virtual path and cannot be directed to a different port.
Support for the IEEE 802.1x standard allows users to be authenticated regardless of which LAN port they are accessing, and provides unique benefits to customers who have a large base of mobile (wireless) users accessing the network.
SSHv2 and SNMPv3 provide network security by encrypting administrator traffic during Telnet and SNMP sessions. SSHv2 and the crypto version of SNMPv3 require a special crypto software image due to US export restrictions
Port Security and unicast MAC filtering secures the access to a port based on MAC addresses. The aging feature of port security removes the MAC address from the switch after a specific timeframe to allow another device to connect to the same port. Unicast MAC filtering allows non-IP packets to be filtered as well.
MAC Address Notification allows administrators to be notified of new users added or removed from the network.
Spanning-tree root guard (STRG) prevents edge devices not in the network administrator's control from becoming Spanning-Tree Protocol root nodCabling 10BASE-T ports: RJ-45 connectors; two-pair Category 3, 4, or 5 unshielded twisted-pair (UTP) cabling
100BASE-TX ports: RJ-45 connectors; two-pair Category 5 UTP cabling
1000BASE-T ports: RJ-45 connectors; four-pair Category 5 UTP cablingLEDs Per-port status LEDs: link integrity, disabled, activity, speed, and full-duplex indications.
System status LEDs: system, RPS, and bandwidth utilization indications.VLAN Support Yes
If something is not on the picture it's not included unless stated otherwise.
Creado con Turbo Lister
La herramienta gratuita para publicar anuncios. Publica tus anuncios de forma rápida y sencilla; controla tus artículos en venta.
Erstellt durch Turbo Lister
Das kostenlose Einstell-Tool. Stellen Sie Ihre Artikel schnell und bequem ein und verwalten Sie Ihre aktiven Angebote.